Challenges
- Standardisation and automation of the creation of accounts and rights.
- Smooth and secure management of rights on arrival, during movements and departure.
- Traceability of assigned rights.
Benefits
- Structuring of access rights allocation processes.
- Agile management of accounts and authorisations.
- Reinforcement of access security levels.
“CyberElements Identity is a structuring solution which enables us to standardise and automate the creation of access rights and securely manage employee entry and exit flows. It’s a pillar in our process security, which also brings real comfort to both the IT team and users.”
About GIMA
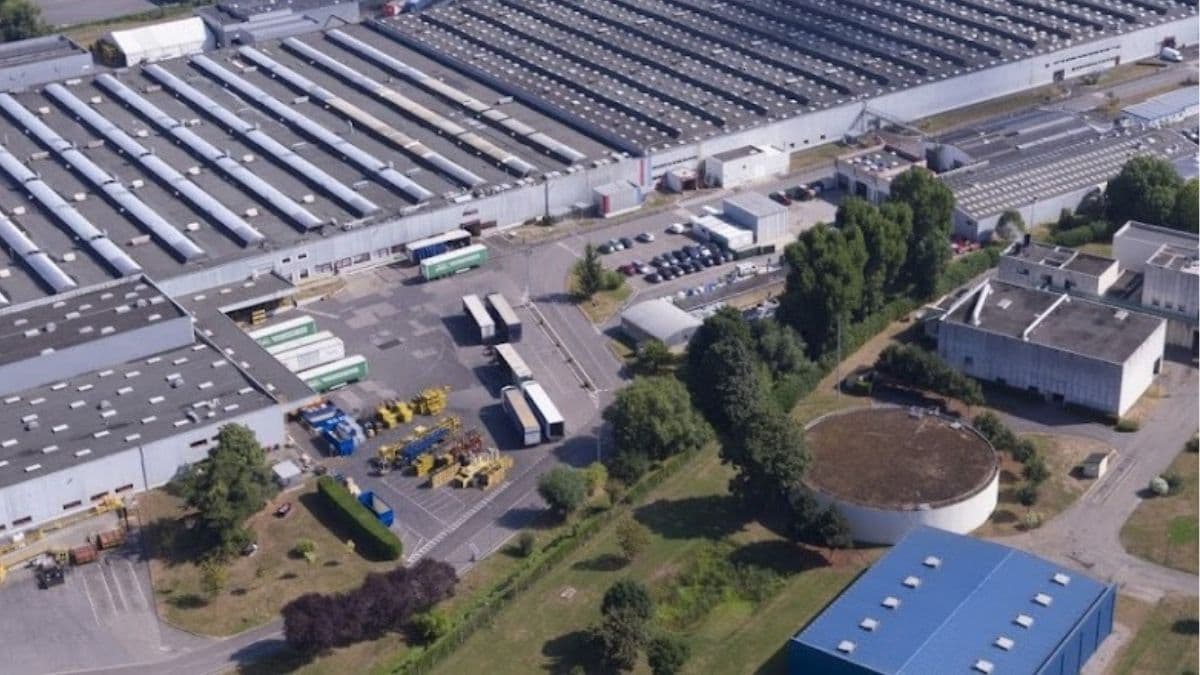
GIMA (Groupement International de Mécanique Agricole) is one of the world’s leading manufacturers of transmission systems for agricultural tractors. GIMA is a 50/50 joint venture between two of the world’s top five agricultural machinery companies: AGCO and CLAAS. GIMA designs and manufactures a wide range of high-tech products (gearboxes and rear axles from 75 to 396 hp) for both manufacturers.
GIMA relies on the expertise and know-how of over 700 employees to produce an average of 20,000 transmissions a year. GIMA’s IT department is made up of 15 people, whose mission is to guarantee the operation and security of the company’s networks, hardware, telephony and industrial applications. The IT team supports the office and workshop teams, ensuring the fluidity and robustness of GIMA’s information system. The main challenge facing GIMA’s IT department was to standardise and automate the creation of accounts and access rights to various IT resources, while enhancing security.
Choosing CyberElements Identity
To tackle this challenge, Frédérique Baroux, Project and Support Manager, and Fabrice Le Bouquin, IT Manager, looked for an identity management solution. CyberElements Identity, an IAM solution whose organisational approach combines the RBAC, ABAC and ORBAC models, was chosen by GIMA. It enabled them to meet the challenge by structuring their processes and modelling their standards.
- Standardisation of AD account characteristics.
- Compliance with existing standards.
- Limit direct access to AD.
- Seamless and secure management of employee entry and exit flows.
- Fluid, secure management of employee mobility to avoid duplication of rights following changes of department.
- Enhanced traceability of account actions throughout the account’s lifecycle: access rights are assigned to the right person at the right time.
Deployed for the past 2 years at GIMA, the CyberElements Identity solution is mainly used to manage AD accounts, file server access rights and business application access. Its integration with the GLPI tool enables ticket generation, ensuring a high level of rigour, particularly through the use of workflows.
Structuring processes for granting access rights
Two repositories feed CyberElements Identity upstream. The IT department therefore worked closely with the Human Resources department to optimise and restructure the account creation and rights allocation processes, streamlining profiles, correcting inconsistencies and eliminating non-standard rights in order to standardise the account creation process.
This collaboration made it possible to list the most frequently used rights, and to create a rights matrix accordingly, resulting in ready-to-use authorisation rules.
Today, the account creation process is fully automated for standard rights. The IT team retains manual allocation for more specific rights, but is working with the various business departments to continue refining the standards and avoid specific rights wherever possible.
Agile account and authorisation management
By automating access rights allocation, the IT department receives fewer access requests to process manually, particularly during employee mobility (arrivals and changes of department). This is an undeniable time-saver for the teams, who no longer have to manage these changes via tickets or telephone. They can concentrate on other projects.
Advanced workflow functions can be used to set up notifications confirming that an employee’s account has been provisioned and to send their manager their login details.
“When an employee leaves, a workflow notifies the IT department that the account has been de-provisioned, through a ticket.”
Based on CyberElements Identity’s ORBAC model, GIMA now benefits from agile and reliable management of personnel mobility (arrivals, departures and so on), enabling rights to be assigned automatically as soon as the change is effective. In fact, certain rights can be managed directly at organisational level, offering speed and efficiency.
Enhanced access security
Interfacing CyberElements Identity with the HR repository ensures data reliability when creating accounts and assigning rights. Repositories can even be resynchronised at any time.
CyberElements Identity offers tracking and control functionalities that enable GIMA to demonstrate, during IT audits, that departure processes are secure, by providing all the evidence expected by auditors.
Thanks to the workflow mechanism, when an employee leaves, a GLPI ticket is created which remains open until the rights are de-provisioned. This avoids dormant accounts and the accumulation of rights, by deleting rights as soon as the employee has left the company.
“CyberElements Identity, with its automation, synchronisation, traceability and workflow functionalities, has become one of the pillars of our process security. It is now an indispensable tool for the IT team.”
Tags
- Client Stories
- IGA
- Industrial & Manufacturing
- OT & Industrial Security
Check other relevant resources
Meurthe-et-Moselle Departmental Council
Delivering a seamless remote working experience for employees.
Hautes-Alpes Departmental Fire and Rescue Service
Securing and simplifying volunteer firefighters’ access to operational applications.
Bièvre Isère Regional Authority
Bièvre Isère authority chose cyberelements to streamline employee integration and enable staff to be fully operational on their first day.
 View All