Get full CyberElements access for free
CyberElements is ready to use from your first sign-in, so you can activate ZTNA, PAM, Agentic AI, IGA and authentication directly from your browser and put real users on the platform from day one.

Sovereign AI Cybersecurity SaaS
Your security team sees one story, your auditors read one log and your users only sign in once.
CyberElements is already running quietly behind armed forces, ships at sea, ministries, insurers and the people who keep satellites in the sky.
Replace the Frankenstack of standalone tools with one platform that shares a Zero Trust access model, designed for compliance on a single control plane.

Waiting months to deploy access control is like buffering a 10-second video on dial-up. Nobody has time for that, especially not with the attacker already inside your guest network.
CyberElements activates from your browser in minutes. Not “fast for enterprise software” fast. Actually fast. Your security team can finally stop explaining delays to the board and start explaining wins.

A single incident should not require a conference call between your ZTNA log, your PAM report, your IGA audit, and your authentication server just to agree on what happened.
CyberElements unifies every access event, human or AI, privileged or standard, into one auditable system. Understanding one incident will not require a degree in digital forensics.

CyberElements grants vendors, contractors and managed service providers application-level access tied to the legitimate identity. The network stays invisible.
Let contractors reach the systems they need without giving them a guided tour of everything else.

Compliance should not require a midnight scavenger hunt through five different log formats, three spreadsheets and an intern’s memory.
CyberElements writes every access action to a single audit trail, tied to one identity, human or AI. NIS2, DORA and EHDS evidence is ready before the auditor finishes their coffee.
Your finance team stops dreading quarter-end. And your security team? They stop living in Excel.

Most tools let you know you’ve been breached. Great. Now what?
With AI analysing behaviour live during the session, CyberElements blocks threats the moment an agent or privileged user acts out of line.
No waiting for the post-incident report. No “lessons learned” meeting about something you could have stopped.
Platform Overview
Four ways CyberElements removes the friction without asking your team to change how they work.
Core Capabilities
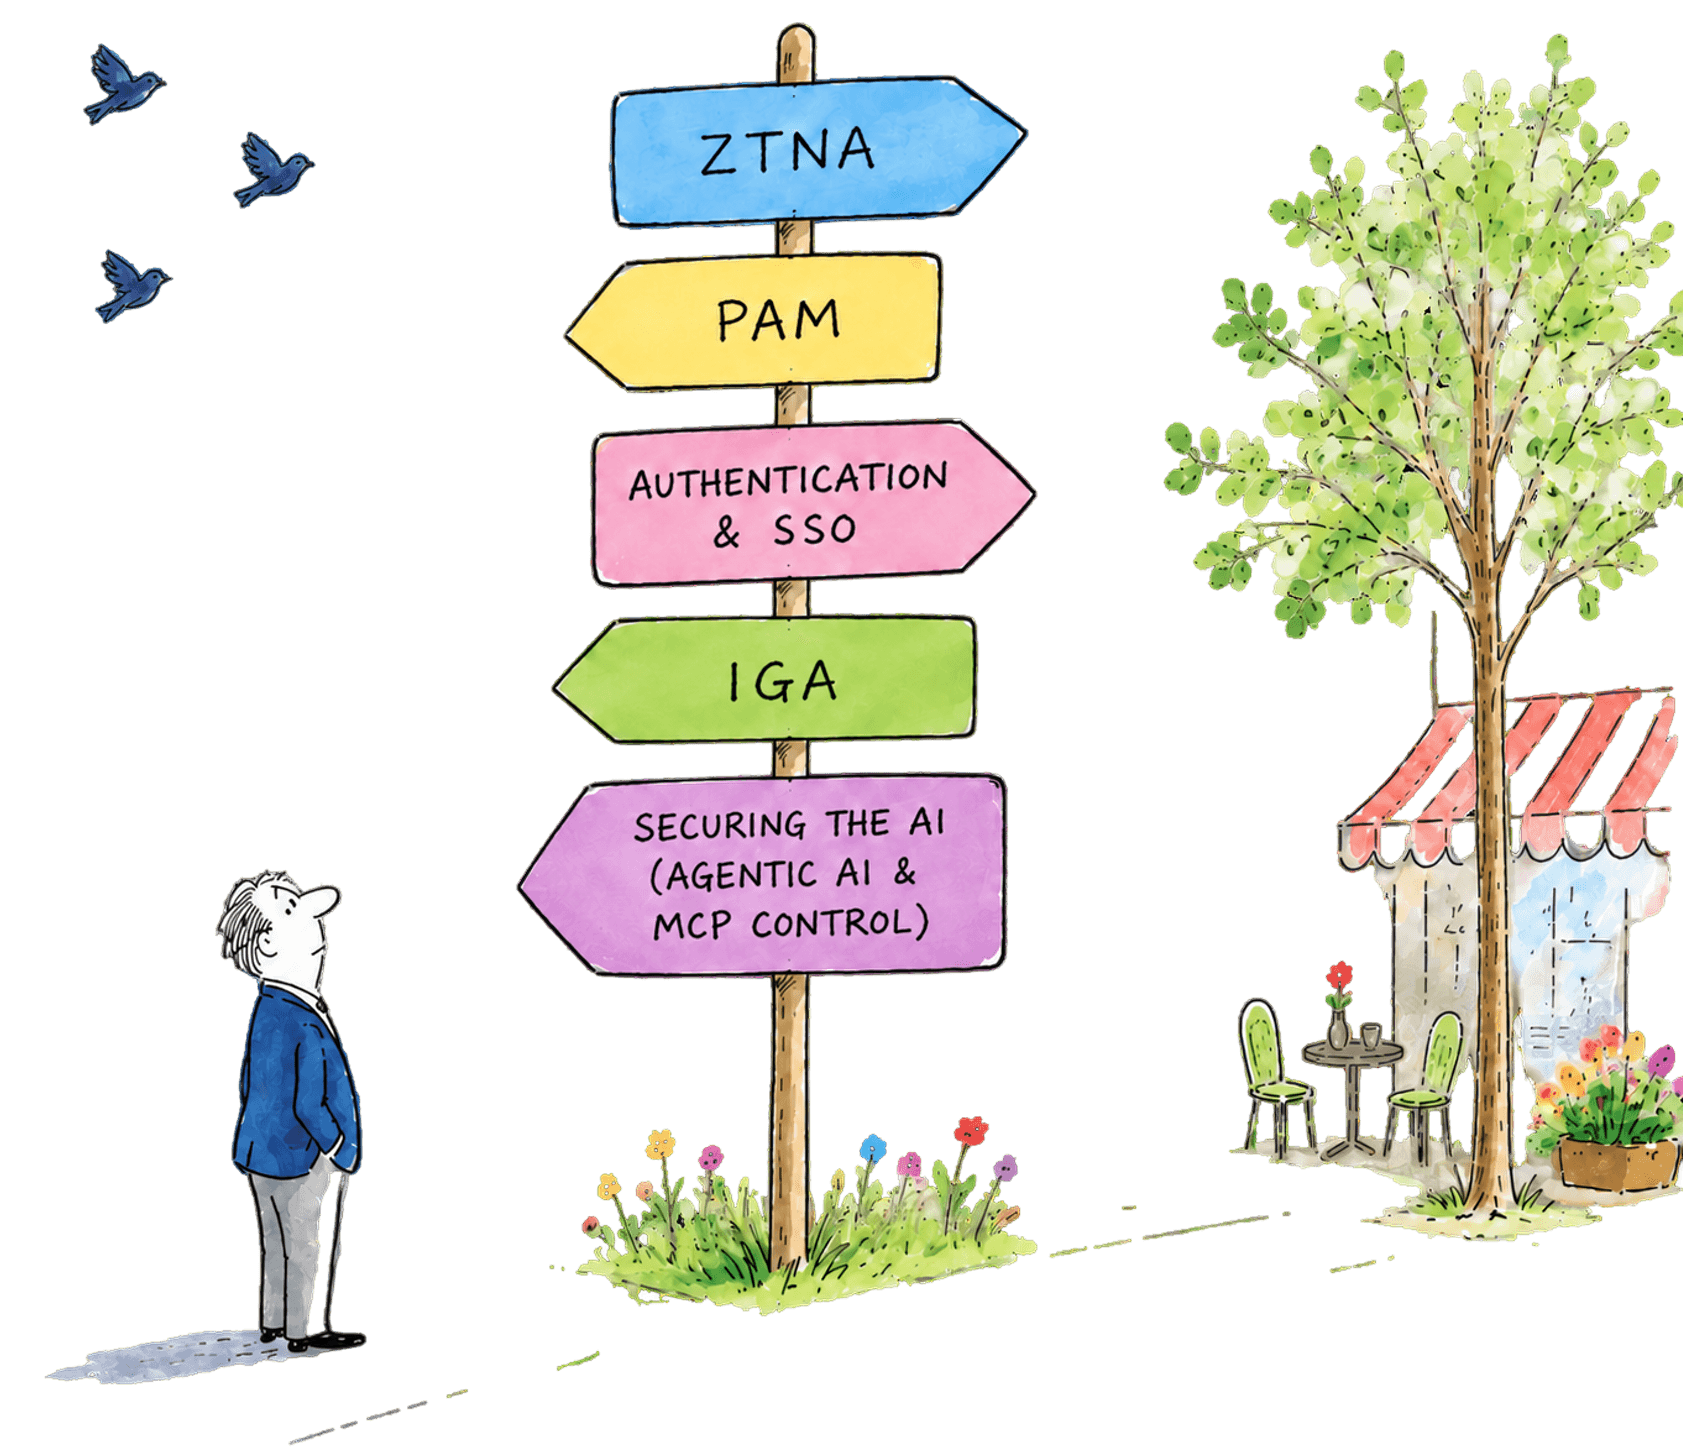
Start with the capability that keeps you up at night.
Set Up
Set up the foundation once, then build the access path you need. Each use case can move independently, so your team can start where the risk, project or deadline is most urgent.
Provide a name, email address and tenant name to create your first account and configure your own production-ready platform for use immediately. Confirm the account within 24 hours to keep it active.
Deploy an Edge Gateway to connect CyberElements SaaS to your datacentre, then connect your on-premise Active Directory or SaaS identity provider.
Add users and groups directly or reuse the ones you already manage. These identities can then be applied to access policies as soon as users connect.
Add applications your workforce needs, then create remote-work policies for them.
Access can change according to context, including whether someone is using a managed company device or a personal computer.
Once the policies are active, employees can reach their authorised business applications through CyberElements from anywhere.
Add the applications contractors need and create their identities locally when they are not managed in your directory.
Apply third-party access policies that can limit them to clientless sessions or require approval before sensitive systems open.
Contractors can then reach only the on-premise or SaaS applications you have authorised.
Deploy the CyberElements client alongside the approved AI Desktop application and activate the MCP proxy on the Edge Gateway.
CyberElements locks the AI Desktop configuration so requests pass only through authorised agents and tools.
AI policies control which applications agents may use, while the console traces each prompt and agent process back to the end user who initiated it.
Deployment
Like an office safe, some systems belong on-site. CyberElements gives you that option across its solutions, with the same technology behind SaaS and on-premises.
CyberElements SaaS is built from the same technology that can run on-premises. That gives customers the speed of SaaS with the reassurance of a platform designed for stricter deployment environments.
Run ZTNA as SaaS and IGA on-premises, or choose the reverse. You can also mix models inside the same product, such as SaaS Identity with Active Directory connectors running on-premises.
Start with one hosting option and change later. Because CyberElements uses the same technology across SaaS and on-premises deployments, your configuration and access history can follow if you migrate.
Integrations
CyberElements integrates with your existing IdP, HR system, applications and cloud environments, reinforcing what you have instead of replacing it. Your dependencies and SLAs stay intact. Your team gains one identity and access model across the rest of the toolchain.
FAQs
Don’t see your question? Visit our full FAQ page.
CyberElements gives you the choice of using our platform as a fully managed SaaS service, manage it yourself or mix both models by module. For example, you can run ZTNA as a service while managing IGA internally. A lightweight Edge Gateway can optionally be deployed inside your environment to connect internal systems to the platform without exposing your network.
The Edge Gateway acts as a filter that sits inside your environment and securely connects local applications to CyberElements. It enables access to internal systems without opening inbound ports and without exposing infrastructure to the internet, so your network stays out of view from outside.
Access is enforced at the access level. Every request is verified, resource and time-bound and identity is continuously validated against behaviour, device posture and context rather than network location.
Yes. CyberElements applies the same Zero Trust access controls across AI, IT and OT environments, including industrial and on-premise infrastructure. The line keeps moving, the segmentation stays clean, and the auditor reads one trail.
Regular user sessions are assessed through device posture, context, behaviour and activity. Lens, our AI session analysis engine, reads each privileged session as it happens, with the ability to isolate, record or revoke the session instantly if conditions change or risks are detected.
All access activity is logged automatically. CyberElements creates a continuous, unified audit trail showing who accessed what, when and why, with NIS2, DORA, EHDS, GDPR and ISO 27001 evidence produced as the platform works.
Yes. CyberElements integrates with your existing infrastructure, identity providers, HR systems and applications, so you can layer enforcement on top of your current stack rather than replacing it.
Yes. Each capability (ZTNA, PAM, IGA, authentication and AI agent control) can be activated independently while still operating under the same Zero Trust access model and audit trail. Start with the part of the platform that solves your noisiest problem and expand as needed.
CyberElements is ready to use from your first sign-in, so you can activate ZTNA, PAM, Agentic AI, IGA and authentication directly from your browser and put real users on the platform from day one.
They recognise CyberElements as a key European player in Identity and Access Management:
We didn’t write these reports. We just earned them.