Administration consoles are at the heart of controlling the information system: they manage servers, backups, endpoints, cloud environments, firewalls, identities and more. Poorly protected, they nevertheless concentrate everything the company holds most valuable. Having access to an administration console provides absolute control over the infrastructure — which is why they represent a real vulnerability for companies.
The most underestimated weak point of the information system
In many organisations, the protection of administration consoles is taken for granted. They are installed, used, and then forgotten.
Yet they represent a real goldmine for attackers: a single access flaw or a poorly managed account can be enough to compromise the entire IT system — often far more quickly than expected.
They concentrate everything the organisation seeks to protect: access, data, and business continuity. And yet few of them benefit from the same level of protection as the systems they administer.
4 questions every CIO or CISO should ask themselves
Can I really guarantee that none of the administration consoles are exposed to the internet?
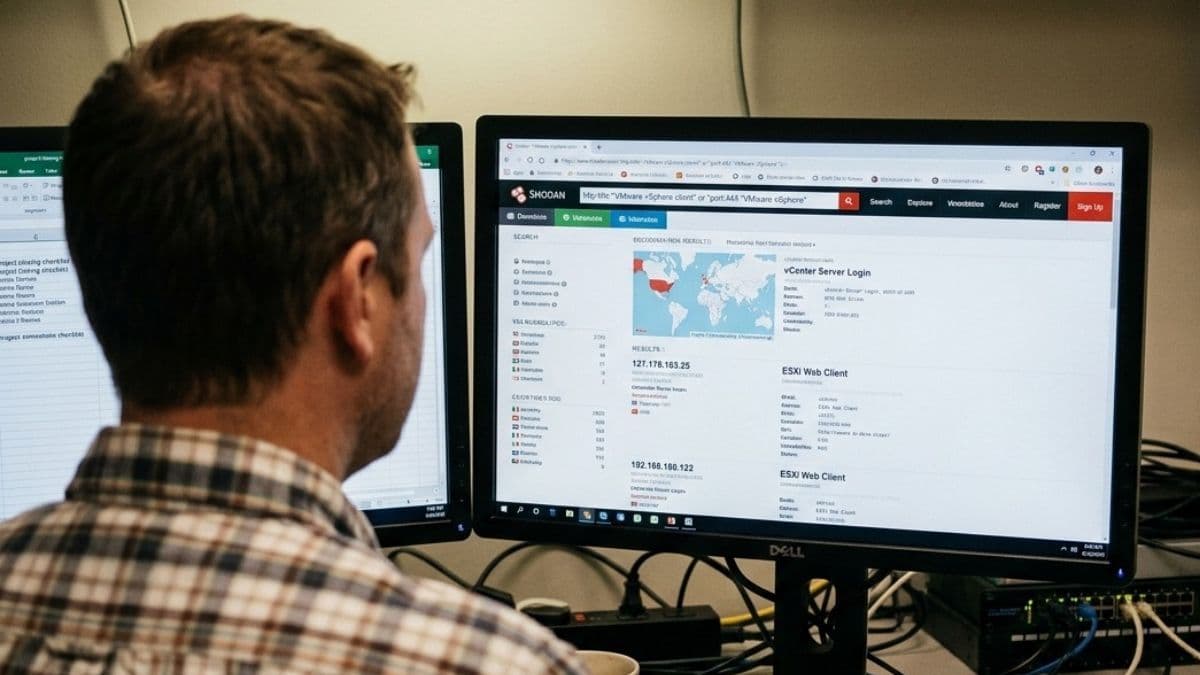
A simple Shodan scan reveals thousands of publicly accessible vCenter, ESXi and firewall interfaces every day. Rarely monitored and often forgotten, administration consoles sometimes even end up being indexed by search engines.
Some consoles also remain accessible after a project is completed, following an audit, or after a service provider leaves — without anyone thinking to disable them.
Can administration consoles be accessed by anyone?
Shared accounts, orphaned accounts, and accounts never revoked after a departure are a classic issue. How many former employees, contractors or interns still retain access that was never removed?
People forget, but IT systems remember — sometimes for far too long. In a context of increased professional mobility, these uncontrolled residual accesses become real time bombs.
Have we properly changed all default passwords?
It may seem unthinkable, yet it is a frequent finding during audits. A default password is like a key under the doormat: everyone knows it is there. And when a former employee knows it too, it becomes a silent — but very real — vulnerability.
Can I confidently say that the administration consoles are not vulnerable to even the most basic attacks?
The example of the backdoor found in certain versions of Webmin clearly illustrates the risk: a vulnerability or compromised component can grant root access to the machine hosting the console. Alarmingly, you do not need to be an expert to exploit this type of flaw — an inexperienced attacker, or even a script kiddie with minimal knowledge, can easily take advantage of it. That is before considering the public bots that constantly scan the web for exposed interfaces and known vulnerabilities.
Forgotten administration consoles are a veritable goldmine for attackers: they are often outdated, unpatched and poorly monitored. From a single initial access point, an intruder can escalate privileges, move laterally across the network, install persistence mechanisms, exfiltrate data, or deploy ransomware. In short, a single poorly protected console is often enough to turn a local intrusion into a full compromise of the IT system.
A systemic risk
These consoles are not just interfaces — they carry ultimate privileges. If they fall into the wrong hands, the entire IT system becomes vulnerable: storage, cloud environments, backups, security policies and the rest.
It is a systemic risk, often invisible until the day it is too late. And on that day, no EDR or firewall can prevent the compromise, because it comes from within.
Recent incidents show this clearly: in the majority of sophisticated attacks, taking control of administration consoles was the key step that led to total paralysis of the IT system. See Fortra confirms “unauthorized activity” hit GoAnywhere MFT.
Regaining control
The question is therefore not so much “are my consoles protected?” as “do I have full control over their use, exposure and access?”
This is where an approach like CyberElements becomes truly valuable, providing a secure, isolated and controlled administration environment, along with complete traceability of access and actions.
CyberElements does not just protect administration consoles: it gives the IT department back the ability to manage administrative privileges confidently, within a controlled and resilient framework.
Just 3 clicks are enough to secure access to a web application, as the recording below shows.
Tags
- Articles
- ZTNA
- Defence & Critical Infrastructure
- Healthcare
- Industrial & Manufacturing
- MSPs
- Public Sector
- Financial Services
Check other relevant resources
Meurthe-et-Moselle Departmental Council
Delivering a seamless remote working experience for employees.
Hautes-Alpes Departmental Fire and Rescue Service
Securing and simplifying volunteer firefighters’ access to operational applications.
Bièvre Isère Regional Authority
Bièvre Isère authority chose cyberelements to streamline employee integration and enable staff to be fully operational on their first day.
 View All